Privacy Policy & DPA
Privacy Policy & DPA
GDPR/UK GDPR COMPLIANT
1. Introduction
This Privacy Policy explains how Sophya Inc. (“SoWork,” “we,” “our,” or “us”) collects, uses, discloses, and protects your information when you access or use SoWork services (sowork.com, app.sowork.com, and related applications).
SoWork is committed to privacy and complies with:
EU GDPR
UK GDPR
BC privacy law
CCPA/CPRA (California)
Australian Privacy Act
We design our systems to minimize data, encrypt data in transit and at rest, and honor all deletion, access, and export rights.If you have questions, you may contact us at:
aloha@sowork.com
2. What Data We Collect and Why
We collect only the data required to provide and improve SoWork. Below is a summary:
Account Information
Name, email, password (hashed), team/organization information
Purpose: Create and manage your account
Lawful basis: Contract
Usage Data
IP address, browser, device type
Interaction events in the app (clicks, features used, session durations) via Google Analytics and Amplitude
Purpose: Improve performance, product quality
Lawful basis: Legitimate interest (EU/UK); analytics consent where required
Workspace Content
Messages, reactions, status text, uploaded images, meeting metadata
Purpose: Provide the SoWork environment and its collaboration features
Lawful basis: Contract
Google Drive Integration Data (optional, only if you connect Google Drive)
Your Google account email, name, and profile picture; metadata of Drive files you choose to share in SoWork (file ID, name, type, icon, thumbnail, link); the OAuth tokens Google issues so SoWork can act on your behalf
Purpose: Let you browse your Drive from inside SoWork, attach files to messages, and let a file’s owner grant a teammate access to that file without leaving SoWork
Lawful basis: Consent (you connect and can disconnect at any time)
Payment Information
Provided directly to Stripe; SoWork does not store full card details
Purpose: Process payments
Lawful basis: Contract
Support Interactions
Emails, chat messages, bug reports
Purpose: Provide support
Lawful basis: Legitimate interest
We do not sell personal information.
3. Lawful Bases for Processing (GDPR/UK GDPR)
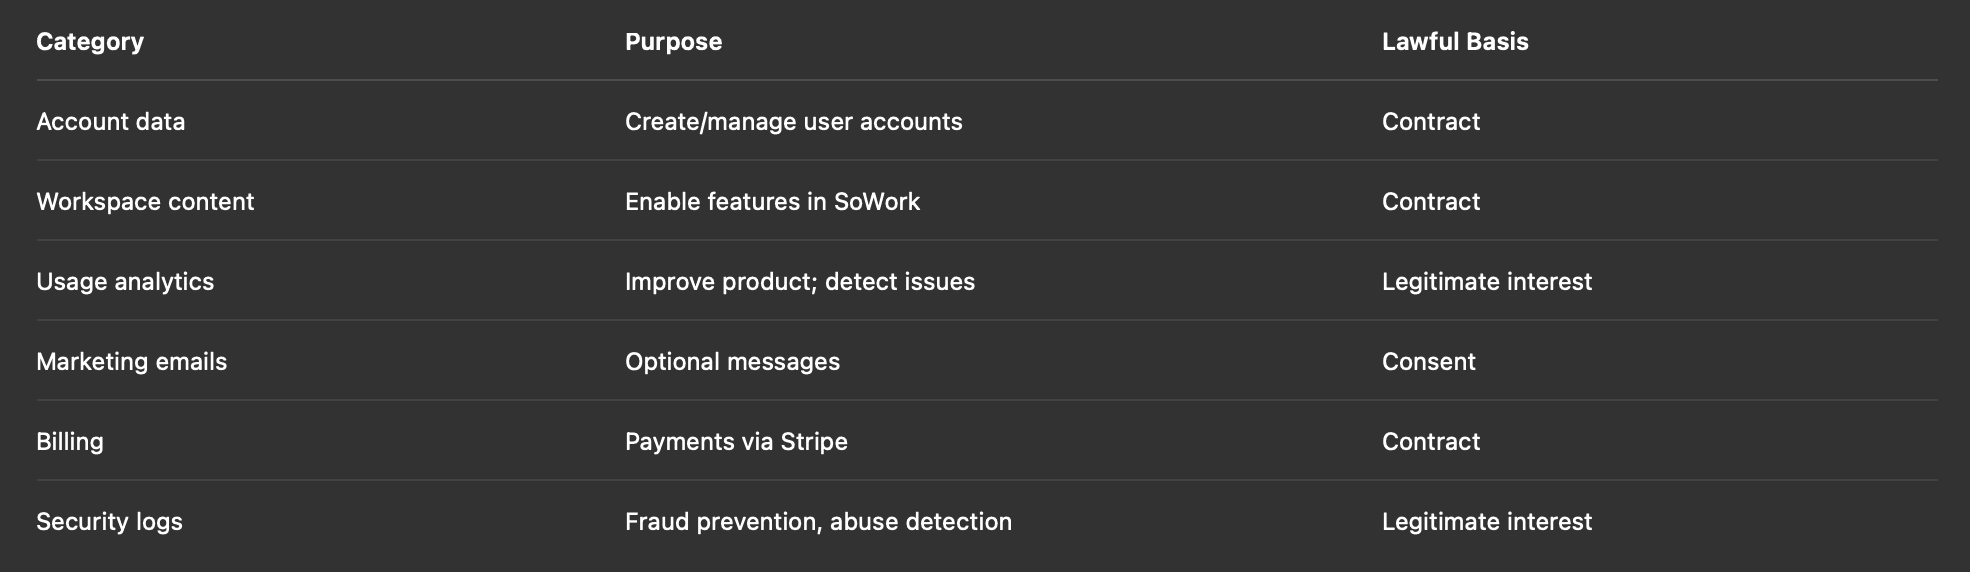
4. How We Share Information
We only share information with vendors necessary to operate SoWork:
Subprocessors
AWS (USA) – infrastructure
Google Cloud (USA) – infrastructure + backups
Stripe (USA) – payments
Google Analytics – analytics
Amplitude – analytics
Each subprocessor is bound by a Data Processing Agreement (DPA) and Standard Contractual Clauses.We do not share information with advertisers and do not sell data.
Google (Drive API) receives requests on your behalf only when you have connected the Google Drive integration; Google acts as an independent controller of your Google account under its own privacy policy.
5.Google User Data and the Google Drive Integration
SoWork offers an optional integration with Google Drive. It is off until you connect your Google account from your SoWork integration settings, and Google shows you the exact permissions requested before you approve.
What we access. With your permission SoWork reads the list of files in your Drive so you can pick one to share, reads metadata for files shared in SoWork (name, type, icon, thumbnail, link, owner, modified time, and whether a viewer already has access), and reads your Google account email, name, and profile picture to show which account is connected. SoWork does not download, store, edit, move, or delete the contents of your Drive files.
Actions we take on your behalf. When a teammate asks for access to a file you shared and you approve the request in SoWork, SoWork creates a “reader” or “commenter” permission on that single file for that teammate, on your behalf. This is the only change SoWork makes in your Drive.
How we store it. OAuth tokens are stored on our servers only, are scoped to your account within one SoWork workspace, and are never sent to your browser or to other users. File metadata is stored on the chat message you attached it to. File thumbnails are passed from Google to your teammates’ browsers through our servers and are not stored.
How we share it. File metadata is visible to the members of the SoWork workspace you shared the file in, the same as any message. We do not transfer Google user data to any other party, and we do not use it for advertising, sell it, or use it to build or train machine learning or artificial intelligence models.
Human access. SoWork staff do not read Google user data except with your consent, to investigate a security issue or abuse, or to comply with law.
How to delete it. Disconnecting Google Drive from your SoWork integration settings revokes SoWork’s access with Google and deletes the stored tokens and integration record. The same deletion runs automatically when you leave or are removed from a workspace, when a workspace is deleted, or when you delete your SoWork account. You can also revoke SoWork’s access at any time from your Google Account permissions page at myaccount.google.com/permissions.
SoWork’s use and transfer to any other app of information received from Google APIs will adhere to the Google API Services User Data Policy, including the Limited Use requirements.
6. International Transfers (EU/UK → USA)
Because SoWork and its infrastructure are located in the United States, your data will be transferred outside the EU and UK.To protect these transfers, we use:
Standard Contractual Clauses (SCCs) approved by the European Commission
UK Addendum to the SCCs
Technical measures including encryption, access controls, and strict role-based permissions
7. Data Retention
We retain data only as long as necessary:
Data Type | Retention Period |
|---|---|
Account data | Until account deletion |
Workspace content | Until account deletion |
System logs | 90 days |
Backups | Up to 90 days after deletion |
Billng records | As required by law (typically 7 years) |
After deletion requests, data is removed from live systems and from backups within 90 days.
Google Drive OAuth tokens and integration records are deleted immediately when you disconnect the integration, leave the workspace, or delete your account, and from backups within 90 days.
8. Your Rights (GDPR & UK GDPR)
If you are located in the EU, UK, or EEA, you have the right to:
Access your personal data
Request deletion of your data
Request correction or updates
Restrict processing
Object to processing
Receive your data in portable form
Withdraw consent at any time
File a complaint with your data protection authority
You may exercise these rights at aloha@sowork.com.
EU/UK Representative (Article 27) Based on our assessment, SoWork qualifies for the exemption from appointing an EU/UK representative because:
our processing of EU/UK personal data is occasional,
does not involve large-scale special-category data,
and presents low risk to individuals.
We continue to monitor this status.
9. Cookies and Tracking Technologies
We use cookies for functionality and analytics.Types of cookies:
Essential cookies – required for login and workspace operation
Analytics cookies – Google Analytics, Amplitude
Preference cookies – remember your settings
Where required, we obtain consent for non-essential cookies.
10. Security
We use industry-standard security measures, including:
TLS encryption in transit
Encryption at rest
Role-based access controls
Regular security reviews
Audit logging
11. Children’s Privacy
SoWork is not intended for children under 13, and we do not knowingly collect data from them.
12. How to Contact Us
COOKIE POLICY (GDPR/UK COMPLIANT)
1. What Are Cookies?
Cookies are small text files stored on your device to make SoWork function properly and improve your experience.
2. How We Use Cookies
Essential CookiesRequired for login, session management, and workspace functionality.
Analytics Cookies used for understanding usage patterns via:
Google Analytics
Amplitude
These cookies are loaded only after user consent where required.
3. Cookie Choices
You may:
Accept all cookies
Reject non-essential cookies
Withdraw consent at any time
Browser settings may also block cookies.
SoWork — DATA PROCESSING ADDENDUM
This Data Processing Addendum (“DPA”) is incorporated into the SoWork Terms of Service (“Agreement”) and applies where SoWork processes Personal Data on behalf of a Customer subject to GDPR, UK GDPR, or similar laws.By using the Services, Customer agrees to this DPA.
1. Roles and Responsibilities
Customer is the Controller of Personal Data.
SoWork is the Processor, processing Personal Data only to provide the Services.
Each party will comply with applicable Data Protection Laws.
2. Customer Instructions
SoWork will process Personal Data only:
(a) to provide the Services,
(b) according to Customer’s documented instructions,
(c) as required by law.SoWork will notify Customer if an instruction appears unlawful.
3. Confidentiality
SoWork ensures personnel with access to Personal Data are bound by confidentiality obligations.
4. Subprocessors
Customer authorizes SoWork to use subprocessors necessary to provide the Services, including:
AWS (USA)
Google Cloud (USA)
Stripe (USA)
Google Analytics
Amplitude
SoWork will impose data-protection obligations on all subprocessors and remains responsible for their compliance.
5. Security Measures
SoWork will implement technical and organizational measures appropriate to the risk, including encryption, access controls, network security, monitoring, and regular reviews.
6. Data Subject Requests
SoWork will assist Customer in responding to data subject rights requests (access, deletion, correction, portability, objection) relevant to data processed through the Services.
7. Personal Data Breaches
SoWork will notify Customer without undue delay upon becoming aware of a Personal Data Breach affecting Personal Data.
8. International Transfers
Where Personal Data is transferred to the United States:
The EU Standard Contractual Clauses (SCCs, Module 2) are incorporated into this DPA.
The UK Addendum applies for UK GDPR.
SoWork will implement supplementary measures including encryption, access controls, and logging.
Execution of this DPA constitutes execution of the SCCs.
9. Deletion of Data
Upon termination of the Services or upon request, SoWork will delete Personal Data from active systems without undue delay and from backups within 90 days, unless retention is required by law.
10. Audit Rights
Customer may:
(a) request summaries of SoWork’s security measures, or
(b) conduct a reasonable remote audit once per year upon written notice.
On-site audits are permitted only if required by law.If such documentation is insufficient for Customer to meet its legal obligations under GDPR or UK GDPR, Customer may conduct a remote audit of SoWork’s relevant systems no more than once per 12-month period, with at least 30 days’ prior written notice.
All audits shall be conducted at Customer’s sole cost and expense. This includes, without limitation:
Customer’s internal costs,
fees of any third-party auditor,
SoWork’s reasonable costs for time, personnel, engineering assistance, and administrative overhead associated with facilitating the audit.
SoWork will require Customer to sign a confidentiality agreement and to agree in writing to reimburse all audit-related costs before the audit begins.
11. Liability and Governing Law
Liability under this DPA is subject to the limitations in the Agreement.
For EU transfers, Irish law governs the SCCs.
For UK transfers, the UK Addendum applies.This DPA is effective automatically and does not require a signature.
Use of SoWork after the effective date constitutes acceptance.